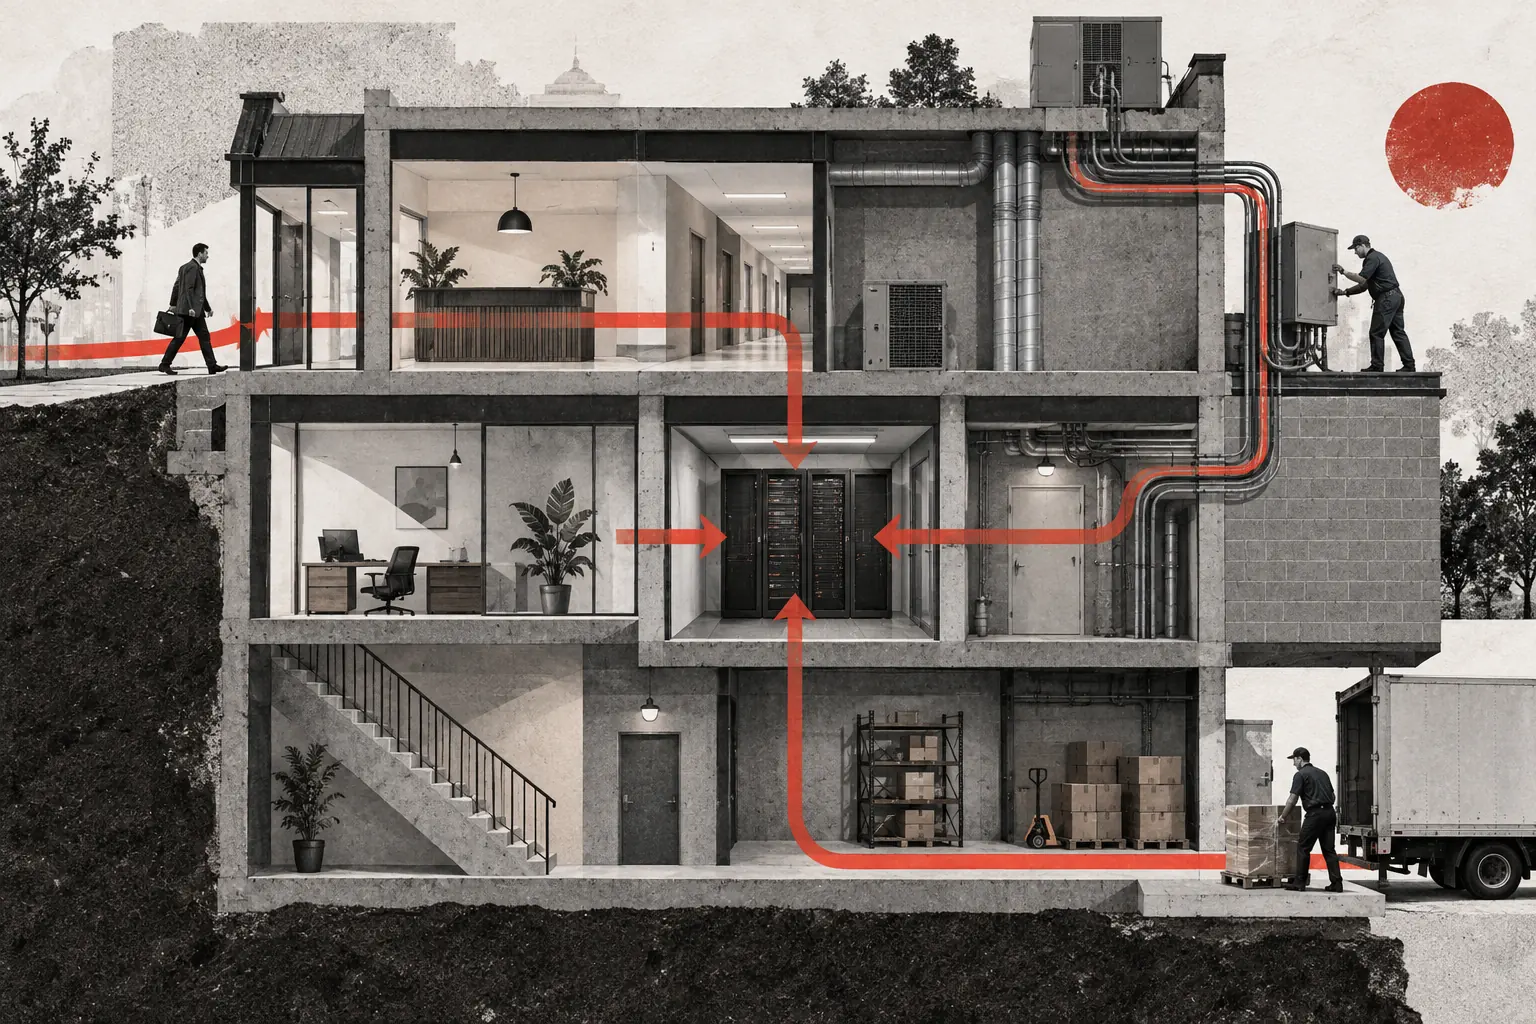
The domain is the address, not the whole building
The short answer: attackers can get in through software reachable from the internet, an account they have taken over, someone they have tricked, or access inherited from a compromised partner. They do not necessarily attack the website. Email, cloud applications and remote access can be the starting point while the homepage carries on looking perfectly normal.
These are not just theoretical possibilities. Mandiant’s M-Trends 2026 reports exploitation as the initial vector in 32% of its investigated intrusions in 2025. That describes its casework, not your personal chance of being hacked. The Verizon DBIR provides another incident dataset; neither gives every business the same ranking of entry points.
Through a vulnerable service
A website plugin, a VPN gateway, a file-transfer service, an old application: something accessible has a weakness the attacker can use. Depending on the flaw, they may get data or control without ever knowing a user’s password. Some campaigns look broadly for affected systems rather than choosing your company by name.
Imagine the polished main website is up to date, but an old customer portal is still running elsewhere. The portal can be the opening. The damage depends on what it can reach and which permissions it holds. Being old or public does not alone prove it is exploitable; the particular flaw and configuration matter.
With a real account that is no longer just yours
Sometimes the attacker simply signs in. A reused password was leaked elsewhere, credentials were stolen from a device, or an existing access was bought from another criminal. An infostealer is malware designed to collect things such as saved credentials and session material. The starting point can be a compromised laptop, not a server.
A stolen session can sometimes be reused without a fresh login challenge, depending on the service’s controls. That is why “we have MFA” is important but not the end of the story. If the account controls email, hosting or domain registration, the attacker may be able to impersonate you, change the site or redirect services within its permissions.
By persuading someone to open the door
A supposed shared document asks you to sign in. A fake support call asks for an urgent action. A bogus update gets installed. The trick is to make an attacker’s request feel like ordinary work. The person may give away a password, approve access or run something harmful without realising what the request actually does.
This is not limited to clumsy email with spelling mistakes. It can arrive by phone, text or chat and use a believable situation. The useful explanation is not “someone was stupid”. It is that an identity check or workflow allowed a convincing story to become real access.
Through someone you already trust
An agency manages the site. An IT provider has remote access. A connected application can read company files. If that partner or integration is compromised, its legitimate access may become the route into your environment. Your own users do not necessarily have to click anything.
For example, a compromised agency account that can publish your website creates a very different problem from a supplier that only receives invoices. “Third party” is not one risk level. What matters is the access the relationship actually grants.
Through a permission or a secret left exposed
A public storage area, an administration interface with no effective authentication, an API that fails to check who may read a record, a valid key accidentally published in code: sometimes there is no spectacular break-in. The system already permits something it should refuse.
An exposed API key can act like a credential, but only with the rights it actually has. A publicly readable file may be a data exposure without giving control of a server. Those are different consequences. “We found something” still needs a precise explanation of what somebody could really do with it.
Then the first opening becomes a bigger incident
An illustrative chain: a stolen email session gives access to account-recovery messages; an insufficiently protected hosting recovery process then lets the attacker replace a page. Another: an exploited server holds an overprivileged service account, extending the damage beyond that one machine. Neither chain is inevitable; permissions and independent checks can stop it.
Ransomware is a possible outcome, not the explanation of how the attacker first arrived. And a lookalike domain used for fraud does not by itself mean your real domain was compromised. An outside scan helps reveal exposed services; it cannot show every stolen session or abused internal permission. So the right question is: which opening could lead to what, here?